OdyxAI brings cybersecurity engineering, continuous quality assurance and reliability practices into the software lifecycle. We assess the risks that matter, build security and testing into delivery, and create the visibility teams need to operate complex systems with confidence. From application and API security to release automation, performance and resilience, we engineer software that is prepared for real use—not just a successful demo.
Identify vulnerabilities, functional regressions and operational weaknesses earlier in the lifecycle.
Bring automated checks, review gates and reproducible evidence into the path to production.
Plan for load, failure, incident response, recoverability and observable system behavior.
Organize controls, test results, remediation records and ownership to support compliance preparation.
Six connected disciplines protect the application, strengthen delivery and help teams operate with control.
Threat modeling, architecture reviews, authentication and authorization checks, secure API design and vulnerability remediation guidance.
Secure development practices, code and dependency scanning, secrets controls, pipeline guardrails and release approvals.
Test strategies, functional and regression suites, API and integration testing, end-to-end automation and defect triage.
Load and stress tests, capacity baselines, bottleneck analysis, performance budgets and scalability recommendations.
Service-level indicators, metrics, logs, traces, actionable alerts, incident runbooks and recovery validation.
Risk assessments, control mapping, evidence preparation and gap remediation aligned to the frameworks relevant to your organization.
Whether you are preparing for a launch, securing a growing platform or stabilizing a critical application, we turn broad concerns into specific technical work.
Review application and API attack surfaces, strengthen identity and access design, address high-priority findings and make risk ownership explicit.
Build automated functional, integration and security checks into delivery pipelines so teams can detect regressions before customers do.
Baseline performance, instrument critical services, validate recovery paths and equip teams with useful monitoring and incident procedures.
The final scope follows the risk profile and architecture of your environment. Engagement deliverables can include:
Our five-stage delivery model brings security and quality into each technical decision, rather than saving them for the end.
Understand architecture, user journeys, critical assets, dependencies, risks, regulatory context and current quality gaps.
Define requirements, assurance priorities, test coverage, control targets, ownership, milestones and measurable acceptance criteria.
Implement controls, automate tests, integrate pipeline checks and make issues visible in a shared remediation backlog.
Validate readiness, execute release gates, confirm monitoring and recovery paths, and complete operational handover.
Track trends, tune alerts, refine tests, revisit threats and improve resilience as systems and usage evolve.
Illustrative tools and reference frameworks, not claims of vendor partnership or certification.
Our product portfolio demonstrates complex interfaces, connected workflows and operational contexts where trustworthy engineering is essential. These examples illustrate product experience; they do not imply that any product has completed an independent security certification or penetration test.
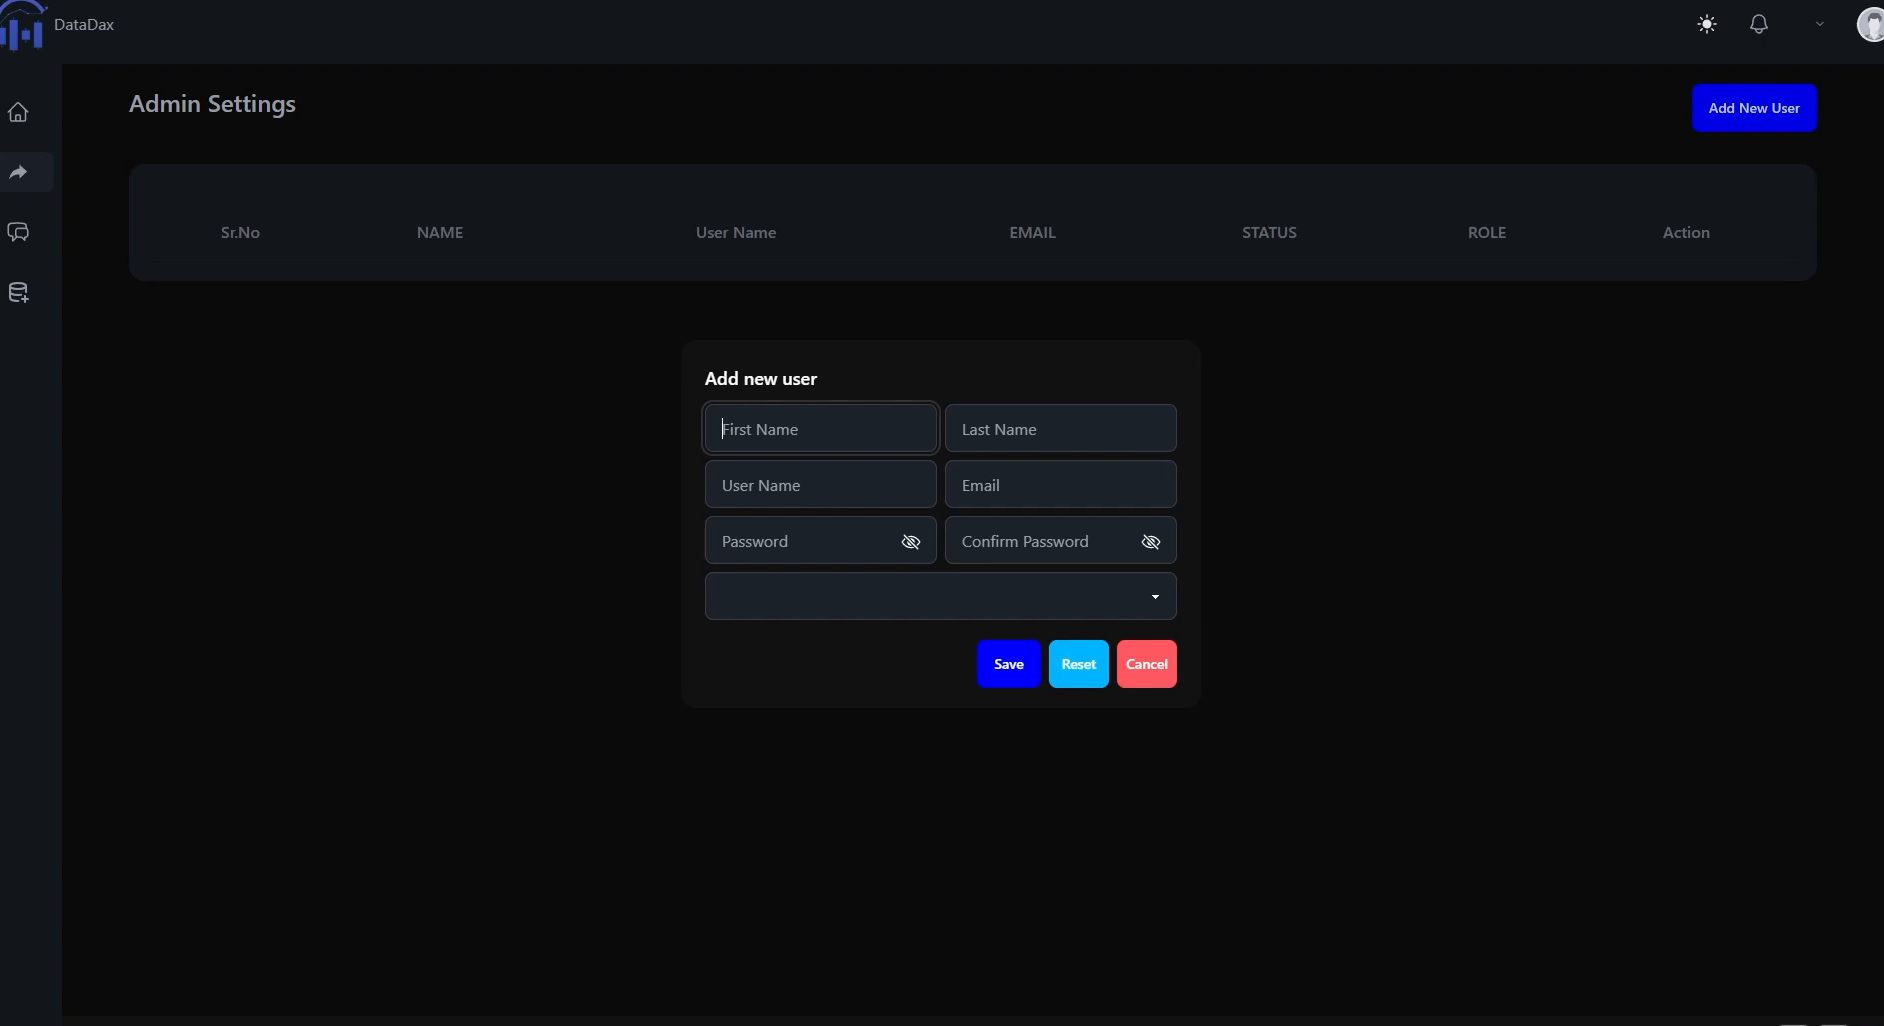
A configurable BI workspace with data-source connections, dashboard sharing and a user-administration interface.
View the product →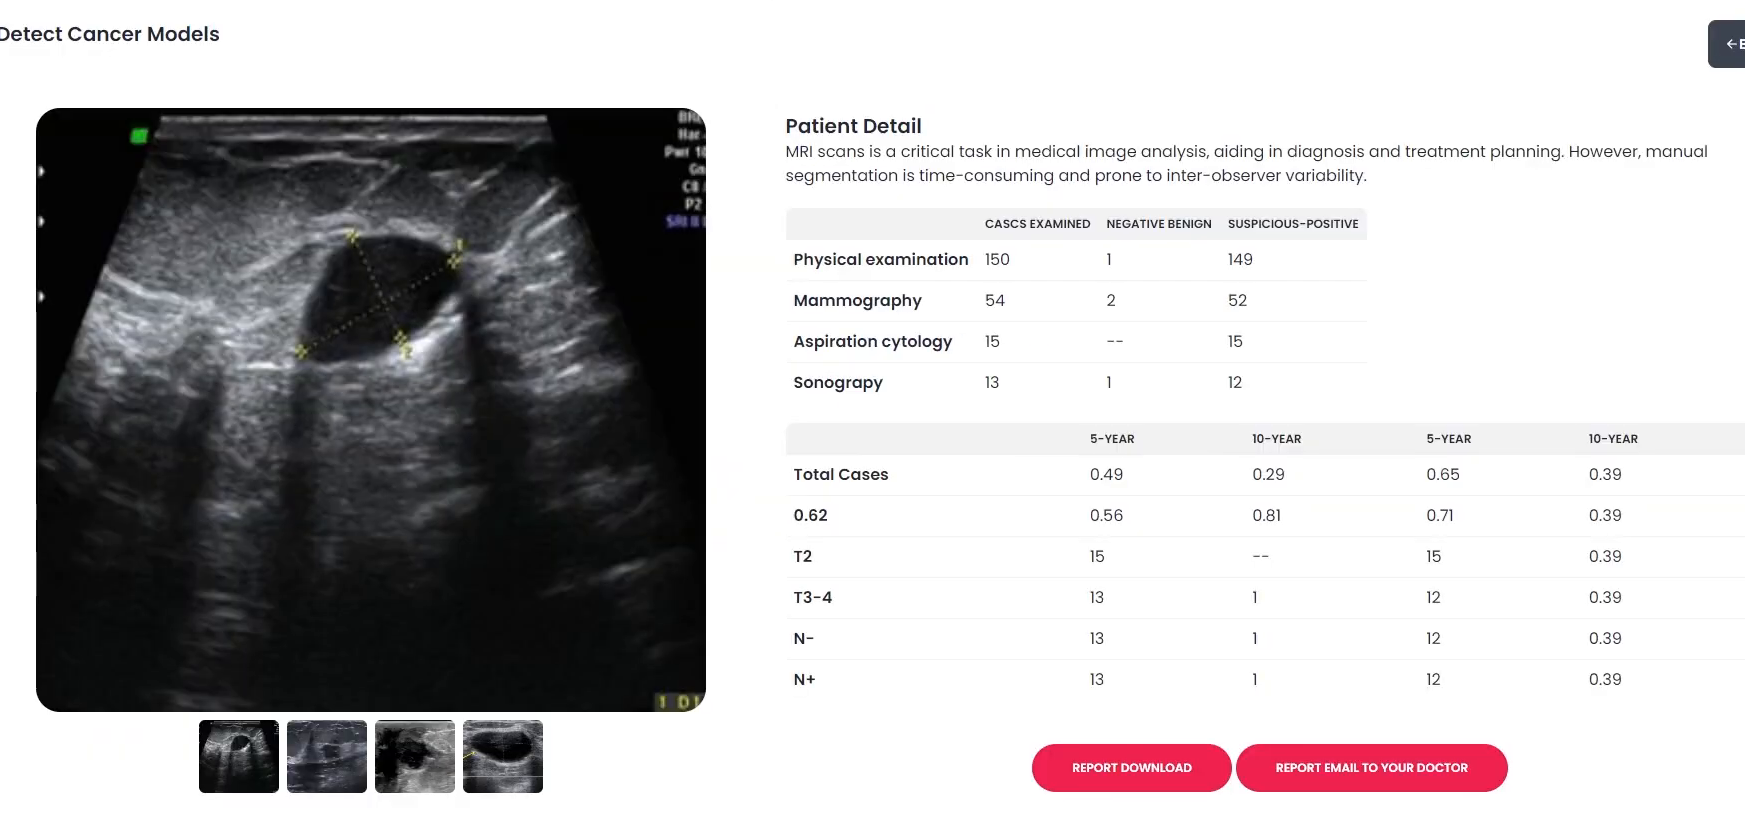
A medical-imaging and risk-questionnaire experience designed around physician-facing review and hospital administration.
View the product →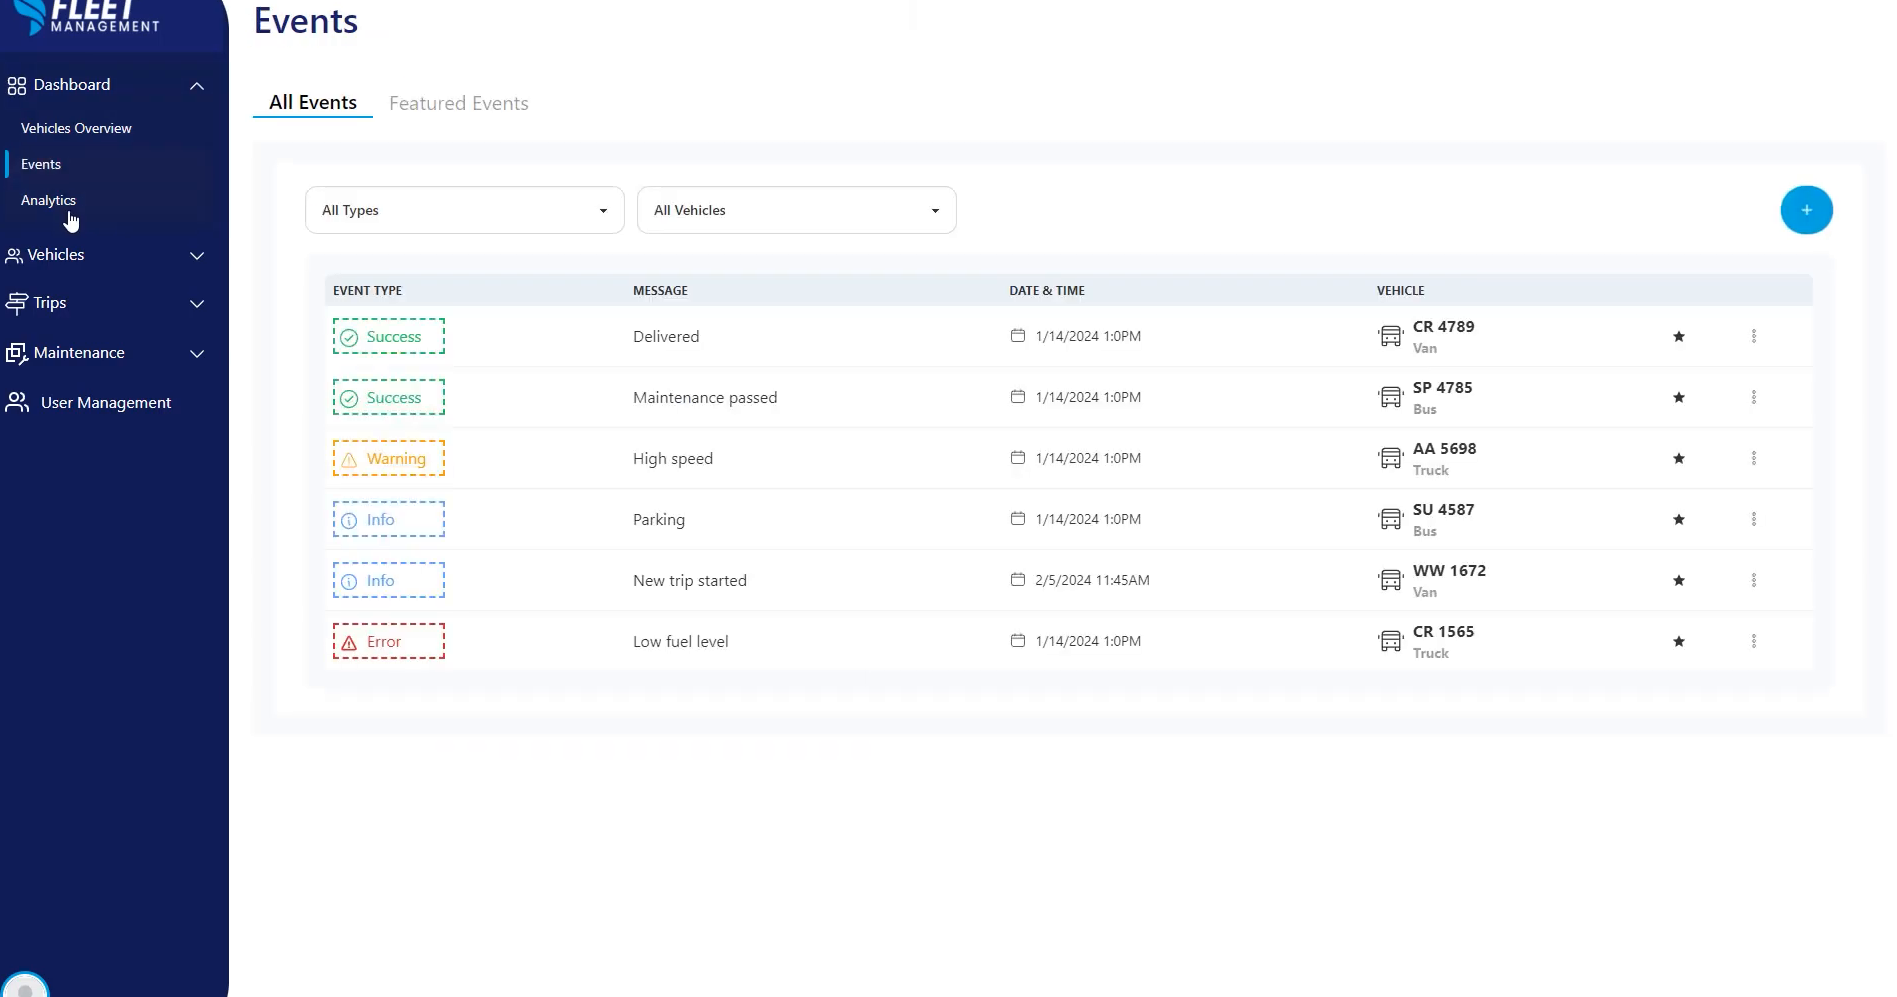
A monitoring interface that brings location tracking, trip information and operational event records into view.
View the product →We can own a scoped initiative, embed specialists alongside your engineers or provide ongoing support under agreed service terms.
A defined security hardening, test-automation, performance or reliability initiative with agreed milestones and outputs.
Embedded QA, application security, DevSecOps and reliability expertise working with your product and engineering teams.
Ongoing monitoring, test maintenance, triage, incident support and iterative improvement under a defined coverage model.
Both. We can start with a current application, API estate or deployment process. An initial assessment identifies exposure, quality gaps and operational risks, then prioritizes improvements according to business criticality and available resources.
We can scope application and API security assessments, testing and remediation support. Formal penetration tests, attestations and external certifications may require qualified independent assessors or accredited auditors. We do not present readiness work as a completed certification.
Depending on scope, requirements can be mapped to recognized references such as NIST SSDF, NIST CSF and OWASP ASVS. We can also help prepare technical evidence for an organization’s ISO 27001, SOC 2 or sector-specific readiness work. Applicable requirements and audit ownership are established during discovery.
Yes. Engagements can include monitoring, alert review, incident runbooks, automated test maintenance, performance tuning and continuous improvement. Availability targets, on-call coverage and response times are agreed separately; no uptime guarantee is implied without a service agreement.
From the first architecture review to the next production release, OdyxAI helps make security, quality and reliability part of everyday engineering. Tell us what you are building—or what needs to work better—and we will help define the next practical step.